

INTERPOL-Led Operation Serengeti III Nets 1,462 Arrests, Recovers Over $105 Million in Africa Cybercrime Crackdown
An international cybercrime crackdown coordinated by the International Criminal Police Organization (INTERPOL) has resulted in 1,462 arrests, the disruption of nearly 11,000 malicious networks and...
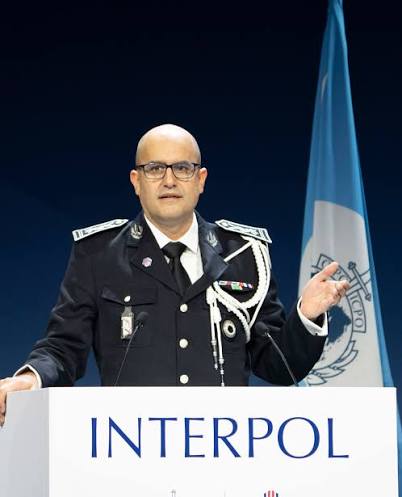
An international cybercrime crackdown coordinated by the International Criminal Police Organization (INTERPOL) has resulted in 1,462 arrests, the disruption of nearly 11,000 malicious networks and the recovery of more than US$105 million in illicit funds across 21 participating countries.
Dubbed Operation Serengeti III, the operation ran from 29 June to 31 August 2026 and targeted cyber-enabled fraud, ransomware, business email compromise (BEC), online investment scams and digital extortion. Investigators identified 65,929 victims, while financial investigations linked the criminal activities to losses exceeding US$385 million.
The operation brought together law enforcement agencies from 20 African countries and the United States, with support from international cybersecurity companies and other private-sector partners. Investigators received intelligence on suspicious domains, internet protocol addresses and command-and-control infrastructure to help identify suspects, map criminal networks and disrupt malicious operations.
According to INTERPOL, several investigations remain active as authorities continue to analyse seized digital evidence, trace suspected criminal proceeds and identify additional suspects.
Cross-Border Fraud Networks Under Investigation
The operation uncovered a range of cybercrime activities, illustrating how fraudsters exploit digital platforms, international payment channels and weaknesses in identity verification to target victims across jurisdictions.
In Uganda, authorities dismantled two transnational fraud networks and arrested 365 foreign nationals allegedly linked to online investment and pension fraud schemes targeting victims across Asia. Investigators uncovered call-centre operations that used scripted communications, fraudulent trading platforms and deceptive websites to persuade victims to invest in non-existent opportunities.
In Angola, authorities dismantled two illegal cryptocurrency mining centres, arrested nine suspects and seized more than 2,000 cryptocurrency mining devices, together with six illegal power transformation stations. INTERPOL valued the seized electrical infrastructure at more than US$1 million.
In Nigeria, authorities arrested a suspect allegedly connected to a large-scale phishing and business email compromise operation that harvested software credentials and collected approximately 2.1 million email addresses. Investigators also recovered a luxury vehicle suspected of having been purchased with criminal proceeds.
A separate Nigerian investigation targeted an international investment fraud scheme promoted through messaging applications. Investigators traced more than US$2.4 million in suspected criminal proceeds, much of which was reportedly laundered through cryptocurrency transactions.
Elsewhere, authorities disrupted a malicious mobile loan application scheme in Tanzania, dismantled a social-media-based vehicle import fraud network in Gabon and arrested 30 suspects linked to a cybercrime operation in the Republic of the Congo.
AML/CFT Implications: Tracing the Proceeds of Cybercrime
Operation Serengeti III highlights the close relationship between cyber-enabled fraud and money laundering. Digital fraud frequently generates proceeds that must be transferred, concealed or converted before perpetrators can use them without immediately revealing their connection to the underlying offence.
The Nigerian investment-fraud investigation is particularly relevant to financial crime compliance because investigators reported that substantial suspected proceeds moved through cryptocurrency transactions. Such activity can complicate the identification of beneficial owners and the tracing of funds across exchanges, wallets and international jurisdictions.
Cryptocurrency transactions are not inherently suspicious or unlawful. However, where transaction patterns are linked to credible indicators of fraud, financial institutions and relevant virtual asset service providers should apply risk-based monitoring, investigate the origin and destination of funds, and comply with applicable suspicious transaction reporting obligations.
The operation also reinforces the need to examine the financial infrastructure supporting cybercrime. Investigations should extend beyond the initial fraudulent communication or compromised account to identify recipient accounts, payment intermediaries, asset-conversion channels and potentially associated beneficial owners.
Business Email Compromise and Corporate Fraud Risk
Business email compromise remains a significant threat to companies because attackers can exploit stolen credentials or compromised email accounts to impersonate executives, suppliers and business partners.
Fraudulent payment instructions may appear legitimate when they originate from compromised accounts or closely resemble established commercial correspondence. Organisations should therefore maintain independent verification procedures for changes to supplier bank details, unusual payment requests and transfers that depart from approved contractual arrangements.
Multi-factor authentication, least-privilege access controls, email security monitoring and timely revocation of compromised credentials are important preventive measures. Finance teams should also have documented procedures for rapidly escalating suspected fraudulent transfers to banks, law enforcement and internal incident-response teams.
The scale of the Nigerian phishing investigation demonstrates why organisations should not rely solely on the number of reported incidents. Stolen credentials and accumulated email addresses can provide attackers with opportunities for further account compromise, impersonation and targeted fraud.
Cryptocurrency, Investment Scams and Financial Investigations
The reported investment scams demonstrate how fraudulent schemes can use messaging applications, fake trading platforms and fabricated investment opportunities to reach victims across borders.
Compliance teams should be alert to transactions inconsistent with a customer’s known financial profile, rapid movements of funds through multiple accounts, unexplained transfers to cryptocurrency platforms and activity involving entities associated with reported fraud schemes.
Effective investigations require a combination of transaction monitoring, customer due diligence, beneficial ownership checks and access to reliable digital evidence. Where justified by the available facts, institutions should escalate concerns under their internal procedures and meet applicable legal reporting requirements.
Asset recovery is also important. Identifying and freezing suspected criminal proceeds at an early stage, where legally authorised, may help preserve funds for potential recovery by victims and authorities. The recovery of more than US$105 million reported by INTERPOL illustrates the financial dimension of coordinated cybercrime enforcement.
Public-Private Cooperation and Threat Intelligence
Operation Serengeti III relied on cooperation between national law enforcement agencies and private-sector cybersecurity partners, including Group-IB, Kaspersky, Fortinet, Team Cymru, Uppsala Security, Cybercrime Atlas, Meta and the Global Anti-Scam Alliance.
These partners contributed intelligence, technical analysis and operational expertise to help identify malicious infrastructure and support investigations. The operation was co-funded by the Global Action on Cybercrime Enhanced (GLACY-e) project, a joint initiative of the European Union and the Council of Europe.
For financial institutions and corporate security teams, the case underscores the value of sharing actionable threat intelligence through appropriate and lawful channels. Timely information about malicious domains, compromised credentials, phishing infrastructure and known fraud patterns can help organisations detect threats before further losses occur.
Such cooperation should be supported by clear information-sharing protocols, appropriate data-protection safeguards and documented procedures for handling sensitive investigative information.
Compliance Priorities for Financial Institutions and Businesses
The results of Operation Serengeti III reinforce the need for organisations to integrate cyber-risk management with financial crime controls. Institutions should regularly test their fraud detection systems, review customer and third-party risk profiles, strengthen authentication procedures and ensure that staff can recognise common social-engineering techniques.
AML/CFT teams should assess whether cyber-enabled fraud indicators are adequately reflected in transaction-monitoring scenarios and suspicious activity escalation procedures. Cybersecurity teams, meanwhile, should ensure that evidence of compromised accounts or fraudulent activity can be shared promptly with financial crime investigators.
Organisations should also maintain incident-response plans covering account compromise, fraudulent payments, data breaches and suspected exposure of customer information. Post-incident reviews can help identify control weaknesses and prevent similar attacks.
Operation Serengeti III represents a major coordinated enforcement effort against cybercrime networks operating across Africa and beyond. The reported 1,462 arrests, disruption of 10,909 malicious networks and recovery of more than US$105 million demonstrate the scale of international cooperation required to investigate digitally enabled financial crime.
For compliance professionals, the operation highlights the importance of linking cybersecurity, fraud prevention, AML/CFT controls and asset-tracing capabilities. Disrupting a cyberattack is only one part of the response; identifying the beneficiaries, tracing the proceeds and preventing further losses are equally important.
With several investigations still active, the next phase will involve continued examination of digital evidence, financial flows and suspected criminal networks. Arrest figures and investigative allegations should not be treated as convictions, and any further enforcement outcomes will depend on the evidence and applicable legal processes.

No Comment! Be the first one.