

Ghana’s Central Bank Tightens AI Compliance Agenda as Banks Face Scrutiny Over Model Risk, Data Integrity and Cybersecurity
The Bank of Ghana (BoG) is developing a directive to strengthen regulatory oversight of artificial intelligence (AI) across the financial sector, signalling tougher expectations for institutions...
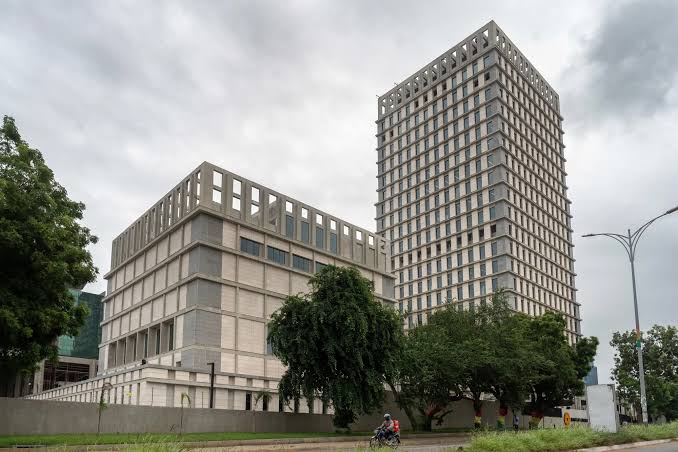
The Bank of Ghana (BoG) is developing a directive to strengthen regulatory oversight of artificial intelligence (AI) across the financial sector, signalling tougher expectations for institutions deploying automated systems in lending, fraud detection, customer service and risk management.
Governor Johnson Pandit Asiama announced the proposed directive at the 43rd Annual General Meeting of the Ghana Association of Banks in Accra. The initiative aims to support responsible innovation while addressing emerging risks associated with data quality, model reliability, cybersecurity and consumer protection.
The development comes as digitalisation increasingly shapes banking operations and financial services delivery. While AI can improve efficiency, expand access to financial services and strengthen fraud detection, poorly governed systems can also produce inaccurate decisions, expose sensitive information, amplify existing biases and create new vulnerabilities for financial institutions and their customers.
Regulatory Focus: Accountability Across the AI Lifecycle
The proposed directive reflects the Bank of Ghana’s intention to strengthen governance over the development, deployment and monitoring of AI systems. The precise requirements and implementation timetable for the proposed standalone directive should be confirmed when the regulator publishes the final instrument.
Meanwhile, the Bank’s revised Cyber and Information Security Directive already addresses AI and machine-learning governance. Its provisions cover model risk assessments, robustness testing, fairness, explainability, change management, performance monitoring, decision logging and independent oversight. The framework also addresses data privacy, confidentiality and third-party technology risks.
This existing framework gives financial institutions a practical starting point for preparing for further regulatory requirements. Banks and other regulated financial institutions should assess whether their current controls cover the full lifecycle of AI systems, from initial approval and data selection to validation, deployment, monitoring and eventual retirement.
Model Risk Management and Automated Decision-Making
AI models used for credit scoring, fraud detection, customer segmentation and transaction monitoring can materially influence financial decisions. If a model is trained on incomplete or unrepresentative data, its outputs may be unreliable even when the system operates as designed.
Financial institutions should maintain documented model inventories, assess the materiality of individual AI applications, conduct appropriate independent validation and establish procedures for identifying model drift and declining performance.
Where AI supports credit decisions or other consequential customer outcomes, institutions should also maintain clear accountability for decisions, appropriate human oversight and mechanisms for reviewing or correcting inaccurate outcomes.
A related Bank of Ghana exposure draft on credit risk management specifically addresses AI governance in credit decisions, including board oversight, reliable data, independent validation, monitoring for model deterioration and human review. Because it is an exposure draft, its proposed provisions should not automatically be described as final binding requirements.
Data Quality, Privacy and Consumer Protection
Data quality is central to the reliability of AI systems. Inaccurate customer records, incomplete transaction histories and poorly governed training datasets can undermine model performance and lead to inappropriate decisions.
Compliance teams should ensure that AI systems operate under documented data-governance policies, with appropriate controls for data accuracy, completeness, access, retention and confidentiality. Institutions should also assess whether personal information is processed lawfully and whether customers are exposed to unfair or discriminatory outcomes.
These safeguards are particularly important when AI is used to determine creditworthiness, flag potentially fraudulent activity or prioritise customers for additional verification. False positives can delay legitimate transactions, while false negatives may allow fraud to go undetected.
Cybersecurity, Cloud Computing and Third-Party Risk
The Bank of Ghana has identified cybersecurity, digital fraud, data protection, cloud computing and third-party dependencies as areas receiving increased supervisory attention. It has also indicated that thematic reviews will examine financial institutions’ implementation of the revised Cyber and Information Security Directive.
AI adoption can introduce additional vulnerabilities through external model providers, application programming interfaces, cloud infrastructure and outsourced data-processing arrangements. Institutions should therefore assess the security and resilience of technology suppliers, define contractual responsibilities, restrict access to sensitive information and maintain incident-response and business-continuity arrangements.
Boards and senior management should treat these issues as enterprise risks rather than matters delegated exclusively to IT departments. Accountability for AI-related decisions, cyber resilience and regulatory compliance should be clearly assigned and subject to regular oversight.
Fraud Prevention and AML/CFT Implications
AI can strengthen anti-money laundering and counter-terrorist financing operations by identifying unusual transaction patterns, prioritising alerts and supporting the analysis of complex financial relationships. However, these benefits depend on the quality of the underlying data, the suitability of the models and the effectiveness of human review.
Financial institutions should validate AI-assisted transaction monitoring against known risks, test whether models detect relevant suspicious activity and monitor false-positive and false-negative rates. Alert-handling decisions should remain appropriately documented, and suspicious transaction reporting obligations must continue to be met under applicable law.
Institutions should also guard against overreliance on automated outputs. An AI-generated alert is not proof of financial crime, while the absence of an alert does not establish that a transaction is legitimate. Final assessments should consider the wider customer and transaction context.
The proposed AI directive is a technology-governance development rather than a standalone AML/CFT rule. Its relevance to financial crime compliance lies in how institutions govern and validate the AI systems used to support existing legal and regulatory obligations.
What Compliance Teams Should Do Now
Banks, payment service providers and other regulated financial institutions should review their AI governance arrangements against the Bank of Ghana’s existing cyber and information security requirements while monitoring the proposed directive’s progress.
Priority actions include documenting AI use cases, assigning board-level oversight, conducting model-risk assessments, validating data quality, testing systems for bias and performance deterioration, reviewing third-party dependencies and maintaining auditable records of automated decisions.
Institutions should also establish procedures for investigating model failures, escalating material incidents, correcting inaccurate outcomes and demonstrating that identified risks are being addressed.
The Bank of Ghana’s proposed AI directive signals a stronger supervisory focus on responsible technology adoption across the financial sector. As AI becomes more deeply embedded in lending, fraud prevention, customer service and risk management, institutions will face growing pressure to demonstrate that innovation is supported by effective governance, reliable data, cybersecurity controls and accountable decision-making.
For compliance professionals, the immediate priority is preparation rather than assuming that a new standalone directive is already in force. Existing requirements provide a foundation for stronger AI governance, while the final terms of the proposed instrument will determine any additional obligations.

No Comment! Be the first one.