

South Africa’s Privacy Watchdog Sends Fresh Compliance Warning as AI and Cyber Risks Mount
South Africa’s Information Regulator is highlighting critical lessons for businesses on data protection, regulatory accountability and compliance as artificial intelligence (AI) and escalating cyber...
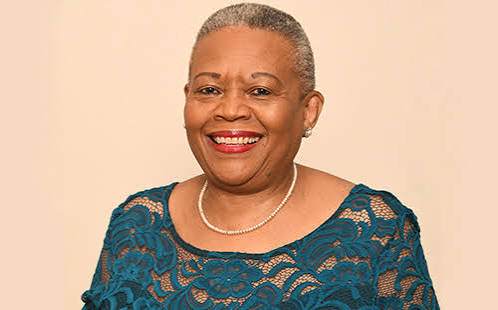
South Africa’s Information Regulator is highlighting critical lessons for businesses on data protection, regulatory accountability and compliance as artificial intelligence (AI) and escalating cyber risks reshape the country’s privacy landscape.
The lessons, highlighted by Advocate Lebogang Stroom, a member of the Information Regulator, underscore the growing importance of effective compliance systems as organisations collect, process and store increasing volumes of personal information.
According to a report by Lexology, Stroom’s reflections draw on the regulator’s first decade and the challenges facing organisations in an increasingly digital economy.
The central message for businesses is that data protection cannot be treated as a box-ticking exercise. It requires sustained management attention, effective internal controls and a clear understanding of the legal obligations governing personal information.
Compliance must go beyond policies
One of the key lessons for organisations is the need to translate privacy policies into operational practice.
South Africa’s Protection of Personal Information Act (POPIA) establishes requirements for the lawful processing and safeguarding of personal information. The Information Regulator is empowered to monitor compliance and investigate alleged violations by public and private bodies.
For businesses, this means ensuring that privacy requirements are reflected in everyday decisions, from collecting customer information to sharing data with service providers and determining how long records should be retained.
Organisations must also understand what information they hold, where it is stored, who can access it and how it moves across departments and external systems.
A compliance framework that exists only on paper may offer little protection when operational weaknesses, unauthorised access or poor recordkeeping expose personal information to risk.
Cyber incidents demand preparedness
The increasing threat of cyber incidents adds urgency to the regulator’s message.
Data breaches can result from deliberate attacks, employee misconduct or seemingly ordinary mistakes, such as sending personal information to the wrong recipient. South Africa’s Information Regulator has advised organisations to identify security compromises, limit their impact, notify the appropriate parties and review the technical and organisational safeguards in place.
Under POPIA, organisations must notify the regulator when there are reasonable grounds to believe that personal information has been accessed or acquired by an unauthorised person. Affected data subjects must also be notified as required by the law.
For compliance teams, effective incident response therefore requires more than cybersecurity technology. It demands clearly assigned responsibilities, escalation procedures, appropriate staff training and the ability to act promptly when a breach is discovered.
AI introduces another layer of accountability
The growing use of artificial intelligence presents organisations with additional questions about how personal information is collected, analysed and used.
Businesses adopting AI tools need to consider whether the information being processed is being handled lawfully, whether appropriate safeguards are in place and whether third-party technology providers introduce additional privacy risks.
These considerations are particularly important where organisations use automated systems to process customer records, assess individuals or make decisions involving personal information.
AI adoption does not remove existing legal responsibilities. Instead, it increases the importance of understanding data flows, assessing risks and ensuring that accountability remains clear when processing activities involve external technology providers.
Regulators are looking beyond formal compliance
The Information Regulator’s broader enforcement work also demonstrates that organisations may face scrutiny where their privacy controls fail in practice.
In August 2025, the regulator issued guidance on handling security compromises, including identifying incidents, mitigating harm, notifying affected individuals and reviewing weaknesses in technical and organisational safeguards.
For boards and senior executives, the implication is that privacy compliance should be treated as an ongoing governance responsibility rather than an issue delegated entirely to IT departments.
Compliance officers, information officers, risk managers and internal auditors must work together to ensure that legal requirements are reflected in operational controls and that weaknesses are identified before they lead to regulatory action.
The message for businesses
The lessons emerging from South Africa’s privacy regulatory experience are relevant to organisations across sectors: effective compliance requires management commitment, practical safeguards, incident preparedness and continuing oversight.
As AI adoption accelerates and cyber threats evolve, businesses that fail to review their data protection arrangements risk exposing themselves to regulatory scrutiny, financial consequences and reputational damage.
For compliance professionals, the priority is clear: build systems that demonstrate accountability, protect personal information and respond effectively when something goes wrong.
In an increasingly data-driven economy, privacy compliance is not simply a legal obligation. It is a test of how responsibly an organisation manages information entrusted to it.

No Comment! Be the first one.