


Nigeria’s SEC Gives Capital Market Operators Until 5 November to Submit Cybersecurity Risk Reports
Nigeria’s Securities and Exchange Commission (SEC) has directed all capital market operators (CMOs) to submit cybersecurity risk assessment reports by 5 November 2026, as part of wider efforts...
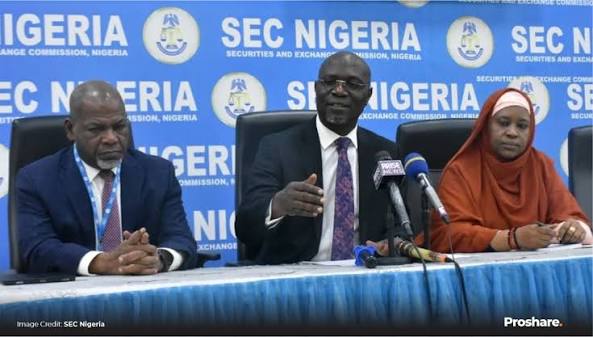
Nigeria’s Securities and Exchange Commission (SEC) has directed all capital market operators (CMOs) to submit cybersecurity risk assessment reports by 5 November 2026, as part of wider efforts to strengthen cyber resilience across the country’s financial sector.
In a circular dated 2 November 2026, the Commission instructed all regulated capital market operators to complete a cybersecurity assessment form through its electronic regulatory portal. Submissions must accurately reflect each organisation’s current cybersecurity risk profile.
The exercise forms part of initiatives led by the Inter-Agency Cybersecurity Technical Working Group of the Financial Services Regulation Coordinating Committee (FSRCC), which aims to improve cybersecurity risk management and resilience across the financial services industry.
According to the SEC, the initiative includes developing a strategic cybersecurity risk management framework, conducting a sector-wide assessment and identifying emerging cyber threats and vulnerabilities.
Other priorities include strengthening information-sharing arrangements between financial regulators, financial institutions, law enforcement agencies and critical infrastructure operators, as well as improving coordination and incident response mechanisms for significant cyber incidents.
The Commission emphasised that the information submitted by capital market operators will contribute to a broader assessment of cybersecurity risks and help identify vulnerabilities across the financial system.
For compliance officers, risk managers and technology teams, the directive highlights the growing importance of regulatory oversight of cybersecurity governance. Firms should ensure that their assessments are accurate, supported by appropriate internal risk information and aligned with their actual security arrangements.
Operators should also review their incident response procedures, third-party technology risks, access controls, business continuity arrangements and cyber risk governance to identify potential weaknesses.
The development reinforces the need to treat cybersecurity as an integral component of operational risk management, regulatory compliance and financial sector resilience.

No Comment! Be the first one.