



FBI Siezes 7 Domains In Blow To Flax Typhoon: U.S. Disrupts China-Linked Cyber-Espionage Infrastructure
The Federal Bureau of Investigation (FBI) and U.S. authorities have disrupted infrastructure associated with Flax Typhoon, a China-linked cyber-espionage group accused of targeting organizations...
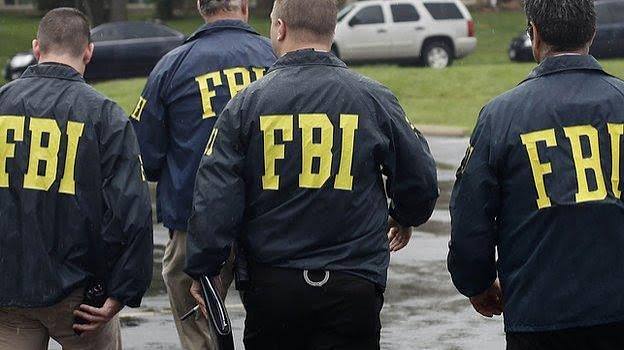
- The FBI and U.S. authorities seize seven domains and disrupt two hacking tools allegedly used by Flax Typhoon to scan vulnerable networks, maintain unauthorized access and steal sensitive information.
The Federal Bureau of Investigation (FBI) and U.S. authorities have disrupted infrastructure associated with Flax Typhoon, a China-linked cyber-espionage group accused of targeting organizations across multiple countries. The operation involved the seizure of seven internet domains and the disruption of two tools allegedly used to identify vulnerable systems, gain access to networks and extract sensitive data.
The action, represents an effort to undermine the digital infrastructure supporting the group’s cyber operations. The targeted domains were allegedly connected to activities involving reconnaissance, vulnerability scanning, spear-phishing and the deployment of malicious tools.
Flax Typhoon has been associated with cyber-espionage operations targeting organizations in the United States and other countries, including entities in critical infrastructure sectors. Reported targets have included a U.S. power company, airports in Japan and Poland, Taiwanese energy-sector companies and Taiwanese universities.
The disruption is intended to make it more difficult for the group to coordinate certain operations through the affected infrastructure. However, the seizure of domains does not necessarily mean that all associated threat actors, tools or compromised systems have been eliminated.
Seven Domains Targeted in Infrastructure Disruption
The operation focused on seven domains reportedly associated with the group’s activities:
– c0cc\[.\]cc
– 98aiblog\[.\]com
– 98aicai\[.\]com
– 98aicode\[.\]com
– outlook3650\[.\]com
– youtubecard\[.\]com
– linkedinns\[.\]net
The domains are presented in defanged form to reduce the risk of accidental access. Their reported association with the operation does not establish that every system or individual that may have interacted with them was compromised.
Domain seizures can interrupt communications, disrupt access to attacker-controlled resources and limit the ability of cybercriminals or state-linked operators to manage certain activities. However, the effectiveness of such measures depends partly on whether the operators retain alternative infrastructure or can establish replacement domains.
For organisations responsible for cybersecurity, the development reinforces the importance of monitoring suspicious domains, reviewing threat-intelligence indicators and investigating connections between internal systems and infrastructure associated with known threat groups.
Microscan and Fishhub: Tools Associated With the Operation
The enforcement action also targeted two tools reportedly associated with Flax Typhoon: Microscan and FishHub.
Microscan was described as a vulnerability-scanning and reconnaissance tool used to identify potential targets. Such capabilities can help attackers discover exposed services, identify weaknesses in network infrastructure and select systems for further investigation.
FishHub was associated with activities including spear-phishing, deploying additional malicious code, maintaining remote access and extracting files from compromised networks.
These capabilities illustrate how cyber-espionage operations can progress from identifying vulnerable systems to establishing access and collecting information. Disrupting tools used during these stages can complicate the group’s operations, although defenders should not assume that a particular tool’s disruption removes an existing compromise.
The distinction is important for incident-response teams. Blocking a domain or identifying a malicious utility may interrupt one part of an intrusion, but organizations must still determine whether attackers previously accessed their networks, established persistence, obtained credentials or transferred sensitive information.
Flax Typhoon and the Challenge of Cyber -Espionage
Flax Typhoon is tracked by cybersecurity researchers as a China-linked threat group associated with espionage-oriented operations. Public reporting has linked the group to Integrity Technology Group, a Beijing-based information technology company.
The group’s reported activities demonstrate the security risks posed by operations that combine reconnaissance, exploitation of vulnerable systems and sustained access to targeted networks.
Unlike attacks designed primarily to encrypt files or demand ransom, cyber-espionage operations may prioritize collecting intelligence, accessing sensitive communications or maintaining a foothold inside strategically important organizations. Such activity can remain undetected when monitoring is insufficient or when attackers use legitimate administrative tools to operate within compromised environments.
Critical infrastructure is particularly sensitive because unauthorized access can expose operational information, disrupt business processes or create additional risks if attackers obtain access to systems supporting essential services.
The reported targeting of energy companies, airports and educational institutions highlights the broad range of organizations that may be affected by intelligence-gathering campaigns. However, the identification of a sector as a target does not, by itself, establish that operational disruption or physical damage occurred.
What the disruption Means for Cybersecurity Defenders
For security operations centres, incident-response teams, compliance professionals and critical-infrastructure operators, the case reinforces several practical priorities.
Vulnerability management and exposure reduction.
Organisations should identify internet-facing systems, prioritize remediation of known exploited vulnerabilities and remove unsupported services from their environments. Exposed routers, network appliances and other connected devices should be patched or replaced where necessary.
Identity and email security
Spear-phishing remains an important method of obtaining initial access. Organizations should enforce multifactor authentication, strengthen email filtering, review suspicious sign-in activity and investigate attempts to obtain credentials through impersonation or deceptive links.
Endpoint and network monitoring
Security teams should examine logs for unusual administrative activity, suspicious command execution, unauthorized remote-access tools and unexplained outbound data transfers. Investigations should also consider whether attackers established persistence before the reported infrastructure was seized.
IoT and network-device security
Organisations should update device firmware, replace unsupported equipment, change default credentials and restrict unnecessary remote administration. Internet-connected devices can provide attackers with additional opportunities to enter or move through a network.
Threat intelligence and incident response
Defenders should consult official advisories and verified indicators of compromise associated with Flax Typhoon. Where relevant indicators are identified, organizations should investigate the surrounding activity rather than relying solely on domain blocking or antivirus alerts.
These measures help address the broader risk of compromise, rather than concentrating exclusively on the seven domains identified in the operation.
Domain Seizures Do Not Guarantee the End of The Threat
The FBI’s reported action illustrates the value of coordinated law-enforcement efforts against cyber-espionage infrastructure. Removing domains and disrupting tools can interfere with an operation’s ability to identify targets, communicate with compromised systems or retrieve stolen information.
Nevertheless, cyber threat actors may attempt to rebuild infrastructure, register replacement domains or adopt alternative methods of maintaining access. Systems compromised before a disruption may also remain vulnerable after the original infrastructure becomes inaccessible.
Organisations should therefore avoid treating the seizure announcement as evidence that their networks are safe. A domain becoming unavailable does not establish that malicious activity has stopped across every affected environment.
For incident responders, the priority remains determining whether a compromise occurred, identifying the scope of any unauthorized access, removing persistence mechanisms, rotating affected credentials and validating that systems have been secured.
A Significant Disruption, Not A Complete Elimination Of Cyber-Espionage
The operation against Flax Typhoon highlights the continuing challenge of defending critical infrastructure and other sensitive organizations against sophisticated, persistent cyber threats.
For law-enforcement agencies, disrupting attacker-controlled infrastructure can impose operational costs and reduce the effectiveness of ongoing campaigns. For organizations, however, the incident reinforces the need for sustained vulnerability management, identity protection, network monitoring and evidence-based incident response.
The seizure of seven domains and the disruption of two associated tools represent a meaningful intervention against the reported operation. The longer-term security impact will depend on whether the disruption prevents further activity, whether alternative infrastructure emerges and whether targeted organizations identify and remediate any existing compromises.
The bottom line: The FBI’s reported action against Flax Typhoon disrupts important parts of a China-linked cyber-espionage operation, but domain seizures alone cannot guarantee that the threat has been eliminated. Organizations should use the development as a prompt to review exposed systems, investigate relevant indicators of compromise and strengthen controls against unauthorized access and data theft.





No Comment! Be the first one.